AI-Discovered PHP Flaws Put Millions of Websites at Risk
AI-Discovered PHP Security Flaw: Critical Internet-Wide Warning
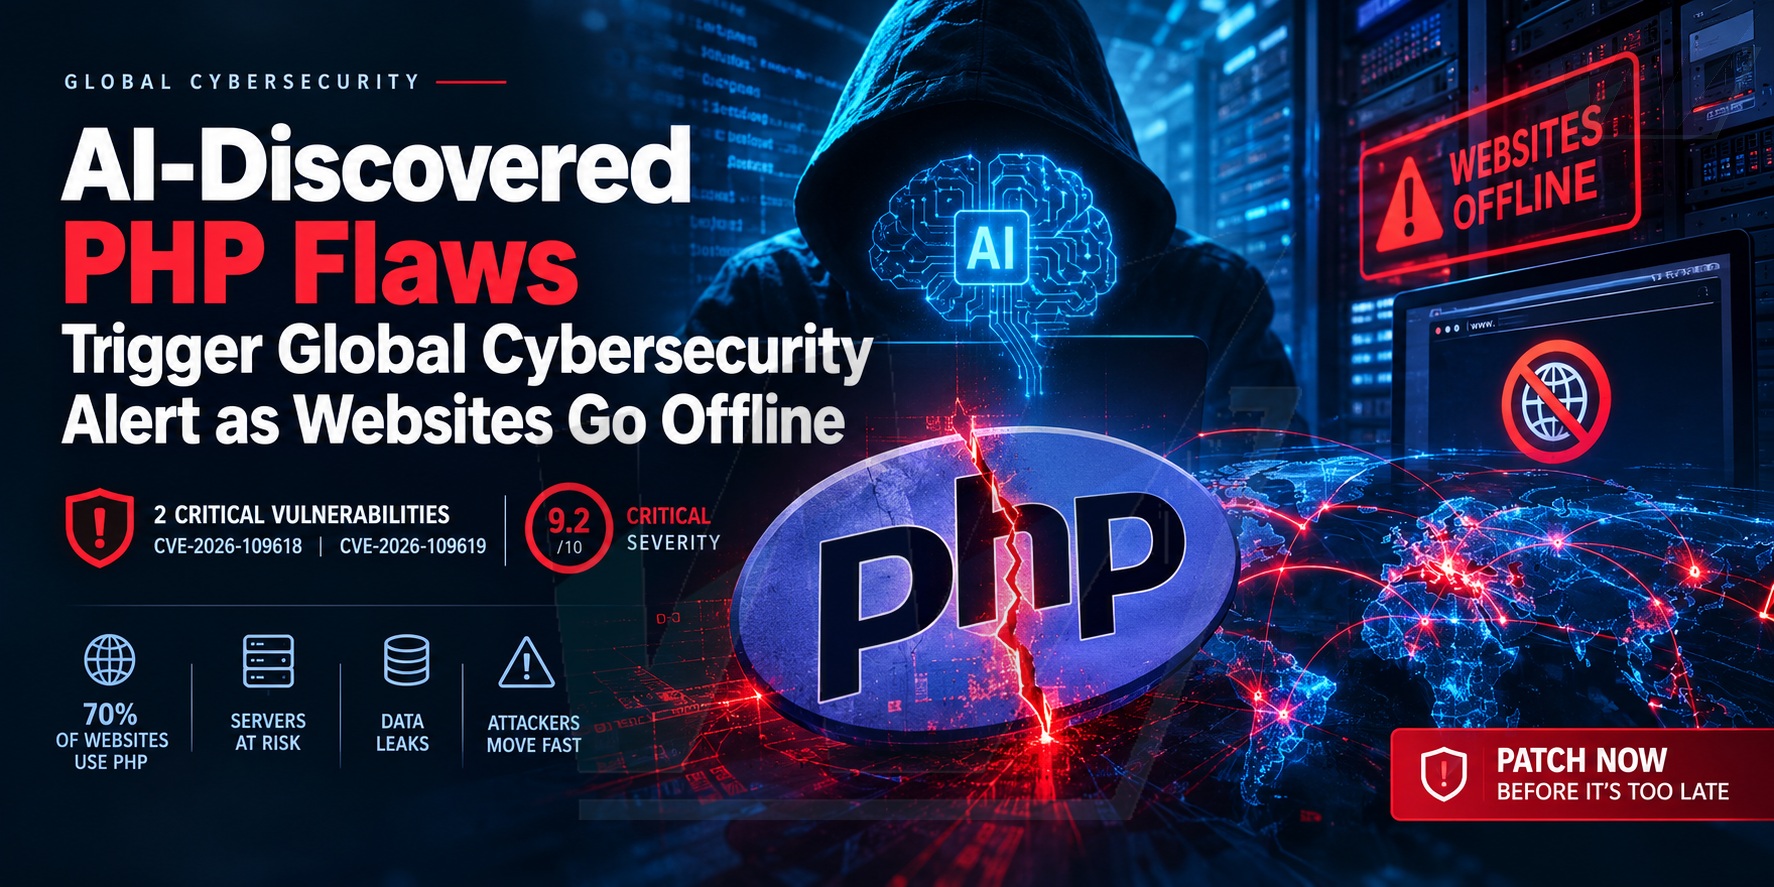
Two critical vulnerabilities rated 9.2 out of 10 threaten PHP-powered servers worldwide. Emergency patches are available, but security experts warn that unpatched systems could become targets as attackers race to develop reliable exploits.
GLOBAL CYBERSECURITY
A hidden weakness in the software powering much of the internet has triggered a global cybersecurity scramble, forcing organizations to patch critical systems, temporarily suspend online services and confront a new reality: artificial intelligence can uncover dangerous security flaws that remained beyond practical exploitation for years.
The crisis centers on two vulnerabilities in PHP, a widely used programming language behind approximately 70% of websites worldwide. Disclosed on October 21, the flaws, tracked as CVE-2026-109618 and CVE-2026-109619, collectively dubbed PHP2Shell, could allow attackers to execute malicious code remotely without authentication, potentially opening the door to server compromise, data theft and service disruption.
Both vulnerabilities received a critical severity rating of 9.2 out of 10 under the Common Vulnerability Scoring System. Security updates have been released, but the emergency is far from over: organizations must still identify affected systems, install the correct fixes and verify that their websites and underlying infrastructure are secure.
A vulnerability hiding in the heart of the web
PHP is not simply another application or website plugin. It is server-side software used to process requests and power websites, content management systems and online services, including platforms such as WordPress, Drupal and Joomla.
That makes vulnerabilities in the PHP engine particularly dangerous. An organization may maintain a secure website and still face exposure if the underlying PHP runtime is vulnerable.
The two flaws involve unsafe memory handling when PHP encounters certain errors during request processing. Under specific conditions, the software may mishandle partially initialized internal data or continue using memory that has already been released. A carefully crafted HTTP request could exploit these conditions, potentially enabling remote code execution or memory disclosure.
The consequences could extend beyond a single website. A compromised server might expose sensitive files, databases or credentials, while attackers could potentially alter content, disrupt services or use the affected machine as a foothold for further intrusions.
The vulnerabilities affect PHP versions dating back to 5.4, according to the published technical advisories. That broad historical reach creates a particularly difficult challenge for organizations operating legacy systems that have not been maintained consistently.
How artificial intelligence uncovered the danger
The discovery marks a significant moment in the changing relationship between artificial intelligence and cybersecurity.
Wiz Research reported finding the first vulnerability on August 19 using AI-assisted research involving Wiz Atlas, Google’s Gemini 4 Argon and OpenAI’s GPT-5.6 Sol. Researchers subsequently demonstrated remote code execution against Drupal and WordPress before reporting their findings to PHP’s security team.
Separately, cybersecurity company Calif identified a critical flaw using GPT-5.6 Sol through OpenAI’s Patch the Planet initiative. Wiz independently discovered and reported both vulnerabilities, while PHP maintainers and collaborating security organizations worked to develop and coordinate fixes.
The findings demonstrate how advanced AI models can help researchers analyze complex code, identify overlooked weaknesses and develop ways to reproduce and verify security problems that might otherwise require extensive manual investigation.
But the same capability creates a race against time. Once a vulnerability becomes public, malicious actors can use technical details and released patches to study the weakness and develop attacks against systems that have not been updated.
The challenge is no longer simply finding a flaw. It is ensuring that defenders can repair it before attackers turn that knowledge into a practical weapon.
Websites go offline as organizations race to patch
The disclosure triggered precautionary shutdowns and service disruptions affecting organizations in multiple countries.
Associated Press reporting identified disruptions involving government websites and services in the United Kingdom, Finland and Japan. Other cybersecurity reporting described a broader response among businesses and public institutions as administrators worked to test and deploy security updates.
Taking a website offline does not necessarily mean it has been hacked. In some cases, suspending a service is a deliberate protective measure while administrators patch vulnerable systems or assess their exposure.
Cloudflare said it deployed web application firewall protections ahead of public disclosure and observed attack traffic targeting customers. The company also reported that attackers were modifying their payloads in attempts to evade its protections.
That evidence illustrates the speed at which the situation can evolve, even as security teams work to contain the threat.
However, the distinction between attempted exploitation and confirmed compromise remains essential. Recorded Future News reported on October 23 that numerous attempted attacks had been observed, but researchers had not established widespread successful exploitation. Some publicly circulating proof-of-concept exploits also appeared ineffective against typical production configurations.
The absence of confirmed widespread compromise is not a guarantee of safety. Attackers may be testing systems, scanning for vulnerable servers or refining their techniques while defenders deploy fixes.
The race against unpatched servers
One of the biggest risks is the vast number of websites and systems whose operators may not know which PHP version they are running.
Large organizations often have dedicated security teams, established update procedures and the resources to test patches. Smaller businesses, independent publishers, personal bloggers and operators of abandoned websites may lack the same capabilities.
Legacy infrastructure creates another problem. Older PHP branches that have reached end of life may no longer receive security fixes from the PHP project, leaving administrators dependent on supported distribution backports or a migration to a maintained version.
Researchers have warned that attackers can scan the internet for vulnerable services and compare patched and unpatched software to understand what changed. That process can help malicious actors prioritize potential targets even without immediately possessing a reliable exploit.
The longer vulnerable systems remain exposed, the greater the opportunity for attackers to discover a workable attack path.
Emergency patches are available: What website owners must do
The PHP development team released security updates on October 21 addressing both critical vulnerabilities.
The published fixed versions are:
-
PHP 8.5.12
-
PHP 8.4.27
-
PHP 8.3.36
-
PHP 8.2.35
PHP 8.1 and earlier are no longer supported by the PHP project. Administrators running those versions should consult their operating-system or hosting provider for any applicable security backports and plan a migration to a maintained PHP release.
The official PHP advisory states that no complete mitigation replaces updating the software.
Website owners, businesses and public institutions should therefore:
- Identify every PHP installation, including forgotten websites, staging environments, internal applications and externally managed hosting.
- Install the applicable security update immediately, following the official PHP advisory and the guidance of the hosting or operating-system provider.
- Verify the actual runtime version used by production applications rather than relying solely on the version installed on a development machine.
- Keep web application firewall protections enabled where available, while recognizing that these are an additional defensive layer—not a substitute for patching.
- Review logs and investigate suspicious activity, particularly unexpected processes, unusual outbound connections, unauthorized file changes or unexplained account activity.
- Assess potential exposure and protect sensitive information, including credentials and customer data, if there is evidence that a system was compromised.
- Maintain tested backups, multifactor authentication and layered security controls to reduce the impact of a successful intrusion.
A new warning emerges after the initial patches
The response has also revealed how quickly the security picture can change.
On October 23, Cloudflare updated its reporting to flag a related issue, CVE-2026-115560, involving PHP’s session upload-progress feature. The advisory indicates that it affects even fully patched releases, including PHP 8.5.12, and is expected to be addressed in a subsequent regular PHP release.
Cloudflare said its existing web application firewall rules cover the issue for customers using the default upload-progress field name, but configurations that change that setting may not receive the same protection.
Administrators should therefore monitor new PHP advisories and hosting-provider notices rather than assume that installing the October 21 updates ends the investigation.
This related issue is a separate development from the two principal PHP2Shell vulnerabilities, underscoring the need for continuing security reviews as researchers uncover additional weaknesses.
The deeper problem: Who protects the software underpinning the internet?
The crisis has renewed questions about the resources devoted to maintaining essential open-source infrastructure.
In reporting published October 23, Reuters quoted PHP Foundation Executive Director Elizabeth Barron describing an organization operating with only one full-time employee, supported by mostly part-time contractors and volunteer board members.
The foundation also acknowledged that the handling of earlier indications of one of the vulnerabilities exposed structural weaknesses in the process. The issues had reportedly surfaced as far back as 2024, but their practical exploitability had not been established.
The episode illustrates the tension between the enormous global reliance on open-source software and the limited resources available to maintainers responsible for keeping it secure.
AI-assisted vulnerability discovery may help close that gap by allowing researchers to examine more code and identify hidden defects faster. Yet more discoveries also mean more reports to investigate, more fixes to review and more pressure on maintainers to respond.
Without sustained investment, improved coordination and effective update practices, the internet’s most widely used software components could remain exposed to risks that are increasingly easy to discover.
The bottom line: The next move belongs to defenders
The PHP2Shell incident is both a critical software-security warning and a glimpse of the next phase of AI-powered cybersecurity.
The immediate priority is clear: identify vulnerable installations, apply the correct patches, check for signs of compromise and continue monitoring new advisories. Organizations that rely on hosting providers must verify that the underlying PHP runtime—not merely their website’s application code—has been secured.
For ordinary internet users, the flaw does not automatically mean their passwords or personal information have been stolen. There is no basis to assume that every PHP-powered website has been compromised. Nevertheless, users should remain alert to suspicious messages, avoid unexpected password-reset links and enable multifactor authentication on important accounts.
The most consequential lesson is that finding vulnerabilities is only half the battle. AI can accelerate discovery, but security still depends on human oversight, responsible disclosure, well-maintained software and the speed with which organizations act.